
Security and trust
Protect sensitive gymnastics data through clear controls and continual assurance.
Our security programme is designed around role-based access, club separation, secure development and the particular responsibilities involved in handling children’s progression, video, injury and welfare information.

Why it matters
Trust requires evidence of effective controls, honest communication about current assurance and a practical roadmap for improvement.
- 01Role-based and club-controlled access
- 02Children’s privacy and data minimisation
- 03Secure development and independent testing
- 04A transparent pre-certification roadmap
Built for UK gymnastics
Support the pathways and club structures used across the UK.
Configure recreational and competitive pathways around your club, British Gymnastics or the relevant home-nation governing body, while coaching decisions remain with qualified people in the club.
British Gymnastics and the relevant home-nation governing body · GBPIdentity and access
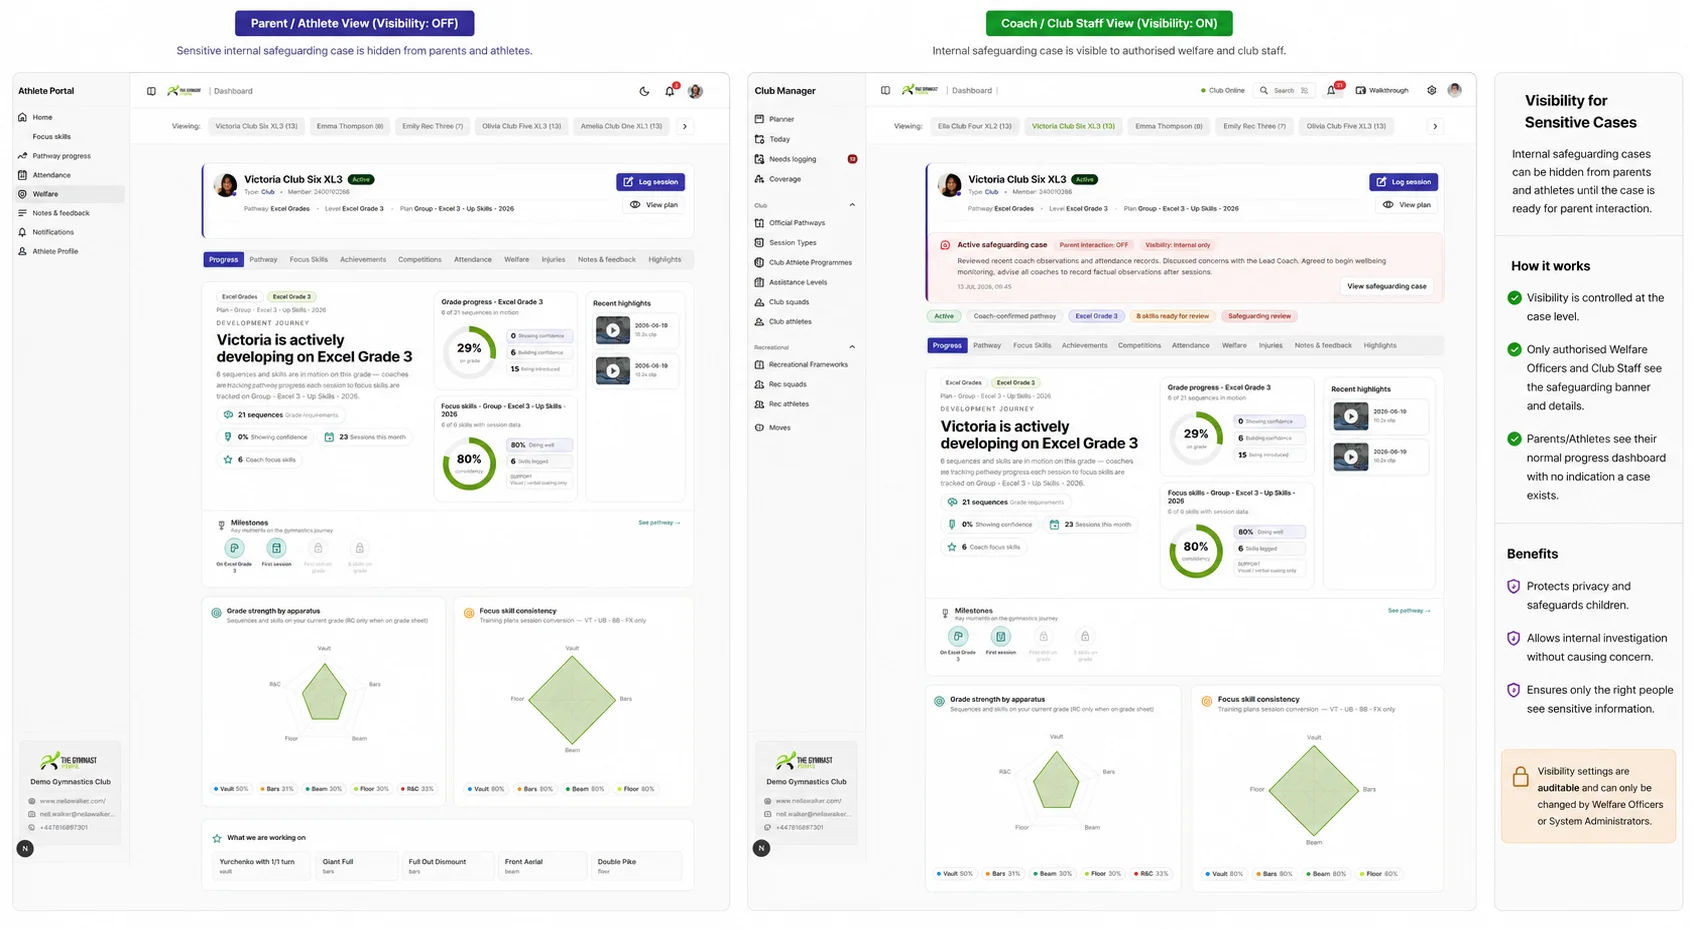
Access follows responsibility.
Club owners, head coaches, coaches, welfare officers and connected families require different views. Permissions are structured around those responsibilities rather than one broad club login.
Production assurance must include deny-by-default rules, cross-club isolation tests, strong administrator authentication, account revocation and regular access review.
- Role-specific permissions
- Cross-club isolation testing
- Guardian relationship controls
- Sensitive record separation
Current assurance
Security claims must follow verified evidence.
This website does not claim SOC 2 or ISO 27001 certification. Before public launch, every statement about encryption, backups, monitoring, hosting location, retention and incident response will be checked against the production environment and documented operating procedures.
The immediate assurance priority is effective access control, secure configuration, restoration testing, security logging and a rehearsed incident response process.
- Verified infrastructure statements
- Backup and restoration testing
- Security monitoring and audit records
- Documented incident response

Secure development and testing
Test the platform before broader use.
The pre-pilot security gate should include automated dependency and secret scanning, Firestore and storage-rule tests, cross-tenant authorisation checks, upload validation, rate limiting and review against relevant OWASP risks.
Before widening the pilot, an independent penetration test and focused Firebase access-control review should be completed, significant findings remediated and the affected controls retested.
- Automated security checks
- Permission-rule test suite
- Independent penetration testing
- Remediation and retesting
Security roadmap
Build assurance in proportion to the risk.
The roadmap begins with a DPIA, controller and processor mapping, retention rules, incident exercises, vulnerability disclosure and a documented subprocessor register. Cyber Essentials is a sensible early external benchmark, followed by Cyber Essentials Plus when the operation is ready.
ISO 27001 or SOC 2 should be pursued when customer scale and procurement requirements justify the ongoing control and audit programme, not used as a substitute for practical early security work.
- Pre-pilot privacy and security gate
- Cyber Essentials pathway
- Recurring independent tests
- Formal certification when justified
Responsible AI
AI supports review without widening access.
AI-assisted overviews must remain subject to the same role and club permissions as the underlying records. Generated summaries should be distinguishable from recorded facts and must not be used to make medical, welfare, safeguarding or coaching decisions.
Before launch, external AI provider terms, data locations, retention and model-training settings must be verified and disclosed appropriately.
- Permission-aware summaries
- No automated safeguarding decisions
- Provider and transfer review
- Human review remains essential
Frequently asked questions
Questions about this part of the platform.
Do AI summaries follow the same permissions as the records?
Yes. AI-assisted overviews must not expose information the user cannot access in the underlying authorised records.
Does the Portal claim ISO 27001 or SOC 2 certification?
No. Current statements reflect verified controls and the assurance roadmap, not unearned certification claims.
See it in your club